
Ad Tech Tides: Building the Same Castle, Just Higher Up the Beach
by Shirley Marschall on 11th Nov 2026 in News
In this weeks’ column, Shirley Marschall looks at ad tech's new battle with Apple, and why the industry didn't see the tide about to turn...
"You don't find out who's been swimming naked until the tide goes out."
Warren Buffett's line fits the moment almost too well, with Apple's latest Safari update pulling the water out from under the identity solutions ad tech built. Turns out a fair number of them have been swimming with very little on.
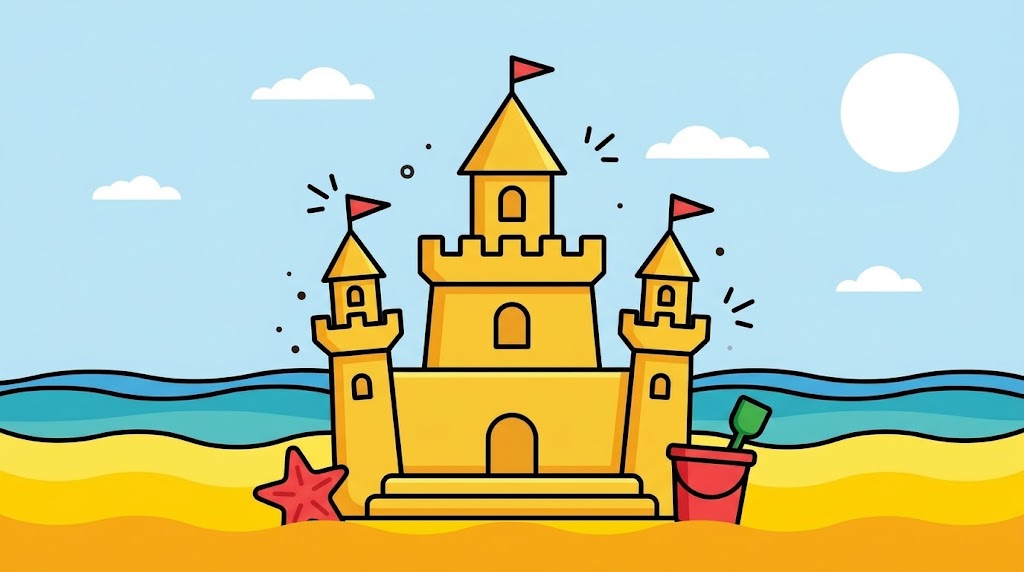
To be fair, when you spend enough time on a beach watching the ocean, you eventually stop noticing the water coming and going altogether. Ad tech has spent plenty of time building on that beach, seemingly forgetting tides exist. And when a browser or a platform or privacy regulators change the rules and the water comes pouring in, the industry collectively moves a few metres further up the sand and rebuilds the exact same castle.
2017: Apple shipped Intelligent Tracking Prevention in Safari. Ad tech answered with first-party cookie workarounds.
2018: GDPR hit Europe. Consent banners became the visible face of compliance, while ad tech went off to build "compliant tracking". At least there were still cookies to rely on…
2020: Safari blocked third-party cookies outright and closed the CNAME cloaking loophole, which had disguised third-party trackers as part of a site's own domain. Google gave cookies in Chrome two years to live. The countdown to a cookieless web had begun.
2021: Apple's App Tracking Transparency made the IDFA opt-in, most users declined, and the industry rebuilt around probabilistic matching and fingerprinting. Google's Privacy Sandbox set off its own round of experiments, from cohorts to alternative IDs, with the same ambition underneath: keep recognising people. Then Google pushed its deadline back for the first time.
2024: Google dropped its plan to phase out third-party cookies.
2025: Google retired most of Privacy Sandbox. Years of preparation for a deadline that never arrived.
Regulators haven't stood entirely still either. Take California's privacy law or the European Commission's Digital Omnibus. Or Australia's privacy regulator, which brought inferred data, third-party enrichment and AI-generated attributes under privacy law… and if social media regulation is any indication, what starts down under rarely stays there.
Still, for a decade, ad tech's roadmap has been written mostly in Cupertino and Mountain View, with regulators supplying the footnotes.
And the industry has survived every tide. GDPR was supposed to "end programmatic". Cookie deprecation was supposed to "end targeting". Neither materialised, and digital advertising adapted. The problem is what the adapting consisted of. Every time, it meant rebuilding the targeting it had just lost in whatever space the latest rule left open, and expecting this version to last.
Then iOS 27 shipped.
Since mid-September, Safari has blocked a list of domains belonging to companies that turn email addresses into cross-site IDs. UID2, ID5, LiveRamp, Permutive, and Audigent all landed on it. Apple stayed silent for a month, then on 19 October the WebKit team published its reasoning, and it read less like an explanation than a policy. The block reaches every updated Apple screen, and there's no clever workaround. Apple's description of the vendors involved is blunt: they're "just there to track you".
This is what the tide going out looks like. Everything built to replicate the cookie assumed the browser would keep tolerating the replica. The newsletter sign-up was always the weak point though. People hand over an email address for a discount code, not to become a node in somebody's identity graph, and that gap is exactly where Apple's intervention lands.
The difference with Google was always incentive. Google needed the open web's ad stack to keep working, which is partly why the cookie tide never fully went out. Apple has no such dependency, but it does have first-party data. Apple Maps started serving ads in August. Safari started blocking identity vendors in September. eMarketer puts Apple's US ad revenue at more than USD$8.5bn (£6.3bn) this year, and some think regulators should take a look.
The walled gardens barely felt it. Meta, Amazon, and TikTok have the logins, which makes them first parties by Apple's own definition, and in The Trade Desk's bug report, Google's bids sailed through on the same Safari page where TTD's were blocked.
This tide clearly went out on the independents, who are already reaching for their buckets and spades. The Trade Desk's ad server, caught in the block by mistake, is back in Safari, though UID2 isn't. IAB Tech Lab, meanwhile, is pushing the industry server-side, which is to say a few metres further up the beach.
Before the next castle goes up, it might help to check what the last one was worth though. Augustine Fou pulled the research together, and it isn't flattering. In one study, researchers tracked IDs across more than 600,000 websites using a crawler that openly declared itself a bot. Seventeen of the 18 identity companies gave it an ID anyway, and one of those IDs followed it across nearly 30,000 sites. In another, an HP campaign aimed at IT decision-makers through bought segments reached people who, more than eight times in ten, had no role in buying technology, and the segments performed worse than random.
Which leaves most of ad tech with identity solutions built on sand it doesn't own, for targeting that never worked as well as advertised. And yet, someone will move the waterline again, and the next workaround will be pitched as the one that holds. Then the water will come back and so will the castles. Maybe the next step isn't finding higher ground, but building on foundations that don't depend on the water staying where it is.
Ad TechCookielessIdentityPrivacyRegulation

Follow ExchangeWire